How to Secure Your WordPress Website: The Ultimate Security Checklist for 2025
Let’s be real—launching a WordPress site is a blast. You tweak the design, add some plugins,…
WordPress malware removal for sites that redirect to spam, show a Google warning or were suspended by the host. I remove the malware, find how it got in, fix that gap and ask Google to lift the warnings.

01Quick answer
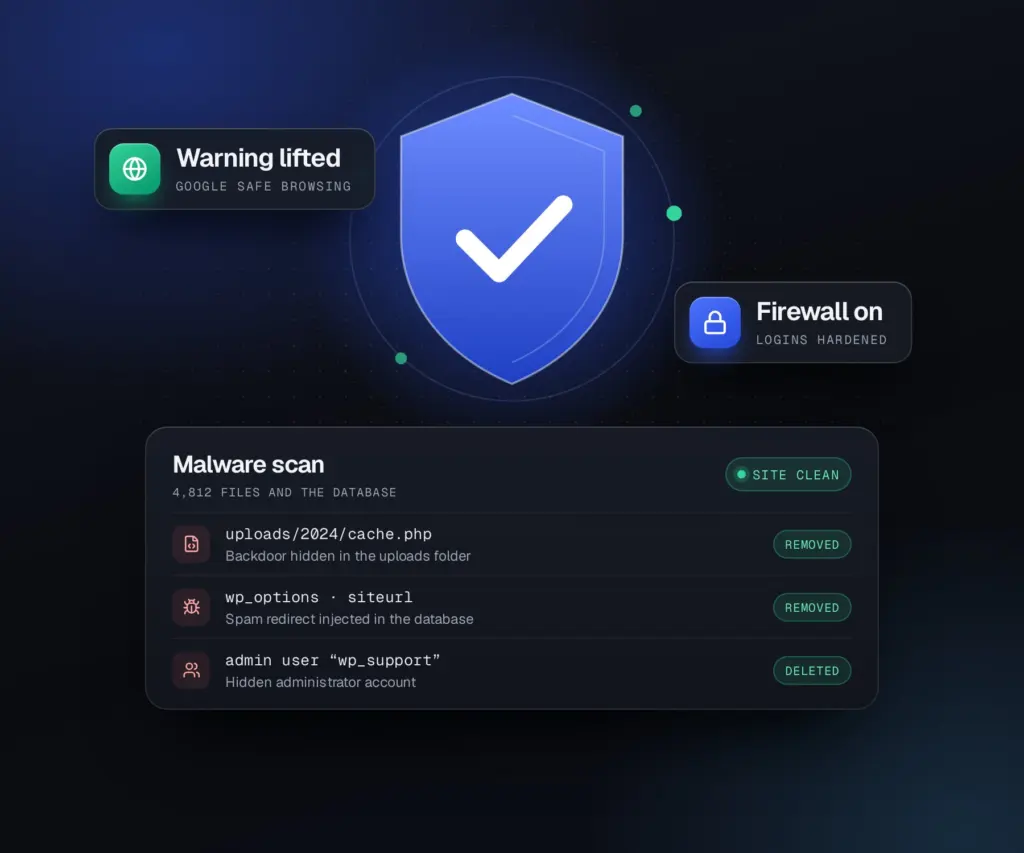
Take a full backup first, then scan files and the database for malicious code and remove it, along with hidden admin users and backdoors. Update everything, change all passwords and security keys, and request a review to remove Google or blacklist warnings. Finally, harden the site so the same hole cannot be used again.
02What you get
A full WordPress malware removal, not a quick scan, so the site is clean and the way in is closed.
03Who it is for
Most of these clients are in the US, UK, Canada and Australia, and I have worked with clients in 70 countries.
Not the right fit if the site is not WordPress. I focus my security work on WordPress.
Spam pages, redirects or a Google warning. I clean it, find how they got in and close it.
Blacklist and host suspension cleared, with a short report you can send on.
A quiet fix under NDA, with hardening so it does not happen again.
04Sound familiar?
Visitors, or only visitors from Google, get sent to pharmacy, casino or scam pages.
Google or the browser warns people away, and your enquiries stop overnight.
A plugin removed the malware once, but the site was hacked again within days.
05Under the hood
The checks that separate a full cleanup from a quick plugin scan.
WordPress core files are compared against the official checksums, and anything that does not match is replaced with a clean copy.
Plugins and themes are replaced with fresh copies from their official sources. Nulled or abandoned ones are removed, since they are a common way in.
The database is searched for injected scripts, spam links and rogue options, and the uploads folder for PHP files that should never be there.
The .htaccess and wp-config.php files, scheduled tasks and must-use plugins are checked, because reinfections often hide there.
Admin, hosting, FTP and database passwords are changed, the security keys are regenerated, and every logged-in session is ended.
Access logs and file dates point to the entry point, such as an outdated plugin or a stolen login, and that gap is closed.
Pharma or casino pages, hidden links and JavaScript injected into posts or theme files are removed, including spam pages Google has already indexed.
Redirect rules hidden in .htaccess, the database or a plugin, including the ones that only fire for phones or for visitors arriving from Google.
A final scan, a check of the Security Issues report in Search Console and a second look a few days later, before the review request goes in.
06How it works
Send a short brief or book a call. I reply within one working day with questions or next steps.
You get the scope, the price and a dated plan in writing before any work starts.
Built and tested on a staging copy, with an update after each milestone.
It goes live at a quiet time, I check everything again, and you get a recorded walkthrough and notes.
07Why work with me
You talk to the person doing the work, from the first call to launch day. The domain, hosting, content and code stay in your accounts, and the price is agreed before anything starts.
More about me08Recent work
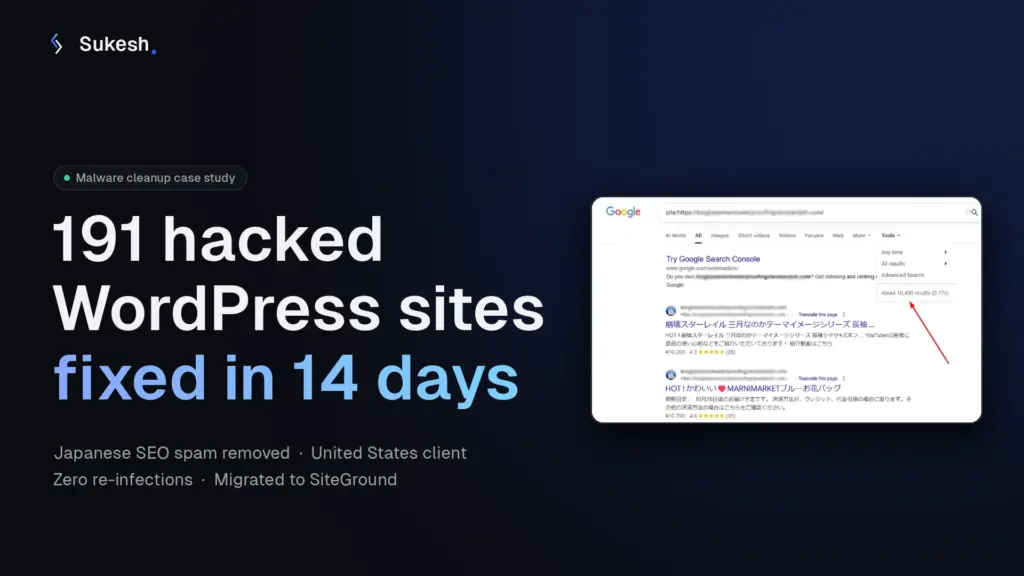
WordPress malware removal case study: I cleaned 191 hacked sites for a US client, fixed the Japanese keyword…
191Hacked WordPress sites cleaned and secured
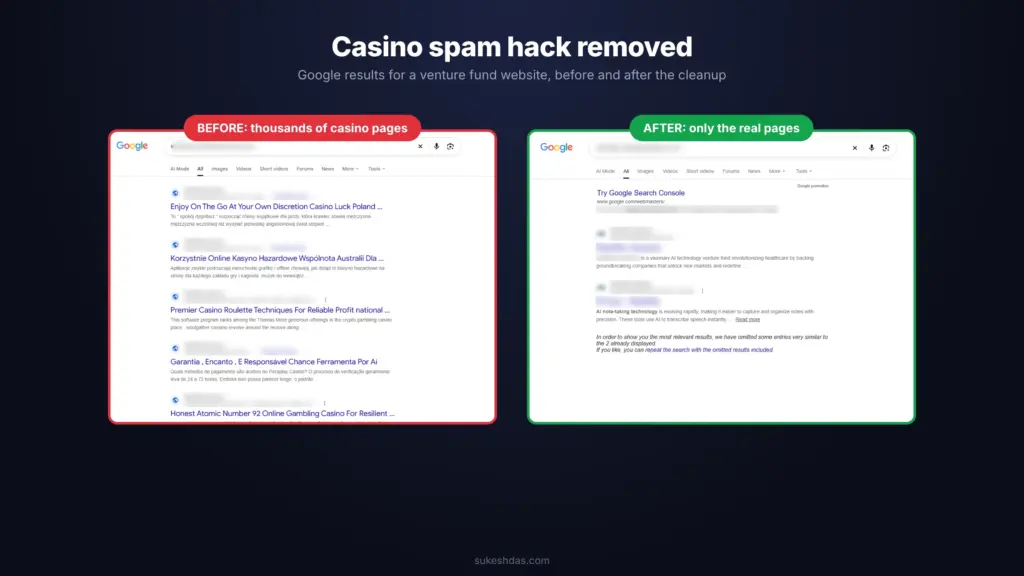
Emergency overnight cleanup of a hacked WordPress site for an AI healthcare venture fund: thousands of casino spam…
1000sCasino spam pages removed from Google
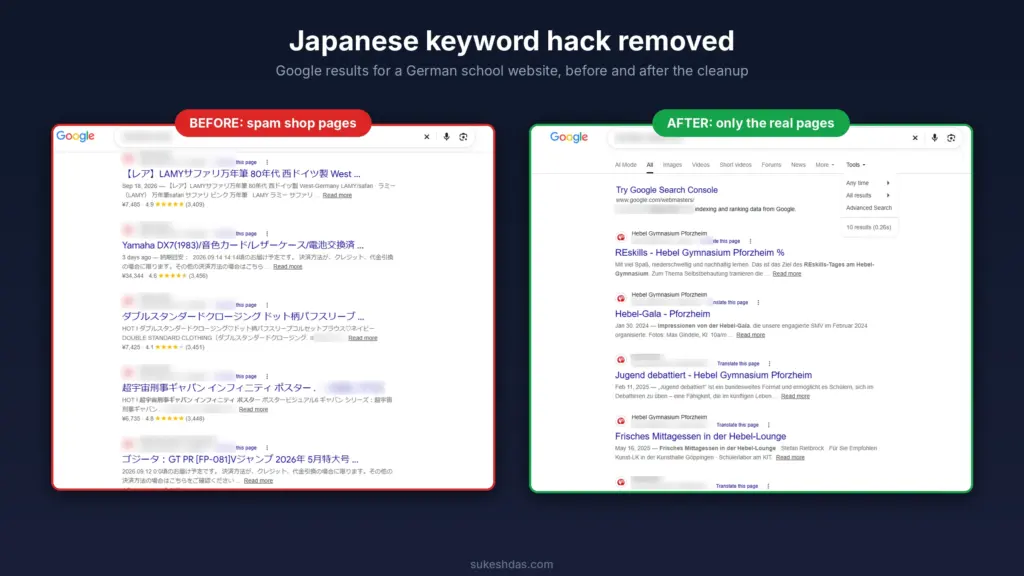
Removed 76,700 Japanese spam pages from Google, cleaned the malware and took back a hijacked Search Console account…
76,700Spam pages removed from Google
09Reviews
Real feedbackEvery review comes from a Fiverr or Google client, shown as written.
We had a very serious issue — our entire server was infected with malware, and three of our websites were hacked. Sukesh did an outstanding job! He not only cleaned the whole server and removed all malicious scripts but…
Our website was infected and I needed a quick turnaround. He originally quoted about a day but worked hard and got us back better than ever in just a few hours. He communicated the whole way through and made great…
I recently had the pleasure of working with Sukesh Das, and I couldn't be more satisfied with the results! After discovering malware on my website and a Google blacklist warning, I was worried about the impact on my…
My WordPress malware removal service starts as soon as I have access and send an update when the site is clean. Google's review of a warning usually takes a few days after that.
No. I take a full backup first and remove only malicious code, users and files, so your pages, posts and orders stay in place.
Usually because the way in was never closed: an outdated plugin, a nulled theme, a weak password or a hidden backdoor. Cleaning without fixing the cause means it returns.
WordPress admin access and access to your hosting account or file manager. Database access helps for deeper infections.
It helps, but it is not a full fix. Plugins often miss infections in the database or in custom files, and they cannot tell you how the attacker got in. Proper WordPress malware removal finds that too.
Redirects to spam sites, a browser or Google warning, strange pages in Google results, unknown admin users, a sudden slowdown, or a warning email from your host.
Google lifts the warning after it reviews the cleaned site. I clean everything first, then request the review through Search Console.
You get a plain report of what was found and fixed. I recheck the site a few days later, and a care plan can keep monitoring, updates and off-site backups running.
Pairs well with
From the blog
Let’s be real—launching a WordPress site is a blast. You tweak the design, add some plugins,…
Booking new projects
Send the address and what you are seeing. The sooner I look, the less damage it does.
Usually replies within 4 hours9 AM to 11 PM, Bangladesh time
 Sukesh Das
Web designer and developer
Today
Hi, I'm Sukesh. Thanks for stopping by.
Tell me a little about your website and what you need. I will reply on WhatsApp with the next steps.
Before you go
I will check your site by hand for speed, mobile, SEO and the things that cost you enquiries, then email you a short report with the fixes in order of priority. No sales call, no obligation.